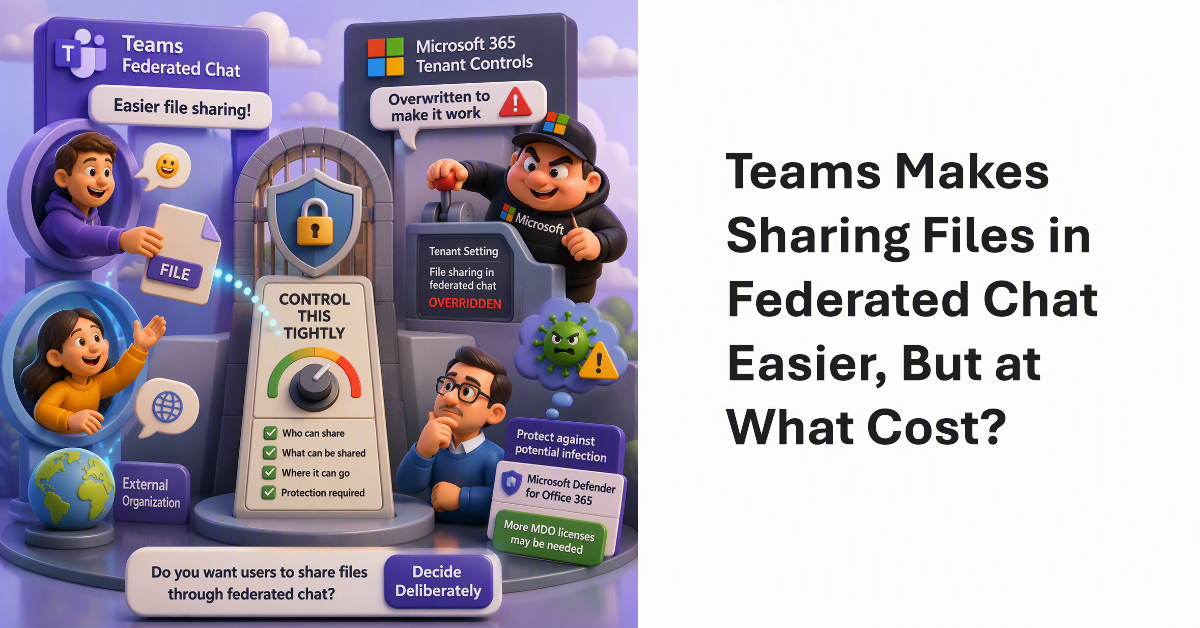
A change to Teams makes it easier for users to share files in federated chat. Sounds good, but Microsoft planned to overwrite existing tenant controls to make the feature work, and that’s wasn’t so good. That issue is now resolved, but the real question is whether Microsoft 365 tenants want users to share files through federated chat. I’m not so sure and would control this facility tightly. Apart from anything else, you might need some more MDO licenses to protect against possible infection.
Monarch client security became an issue last year when a German website reported some issues. It turns out that the reported problems are mostly hyperbole, but that hasn’t stopped them persisting, especially when email client competitors like Proton weigh in. It’s regrettable that much of the commentary is based on an incomplete understanding of how Monarch works, but Microsoft doesn’t help themselves by not explaining the facts.
The CISA report titled “Microsoft Office 365 Security Observations” makes five recommendations to improve security of an Office 365 tenant. The recommendations are valid, but competent administrators won’t take long to implement them. In fact, the worst thing is that consultants brought in to help organizations didn’t seem to have much expertise in securing Office 365.
Hanging on to old email habits is a bad idea, especially if you use a cloud service like Office 365 where Microsoft introduces a steady stream of new features. The worst bad habit is password sharing. It’s time to stop this now.
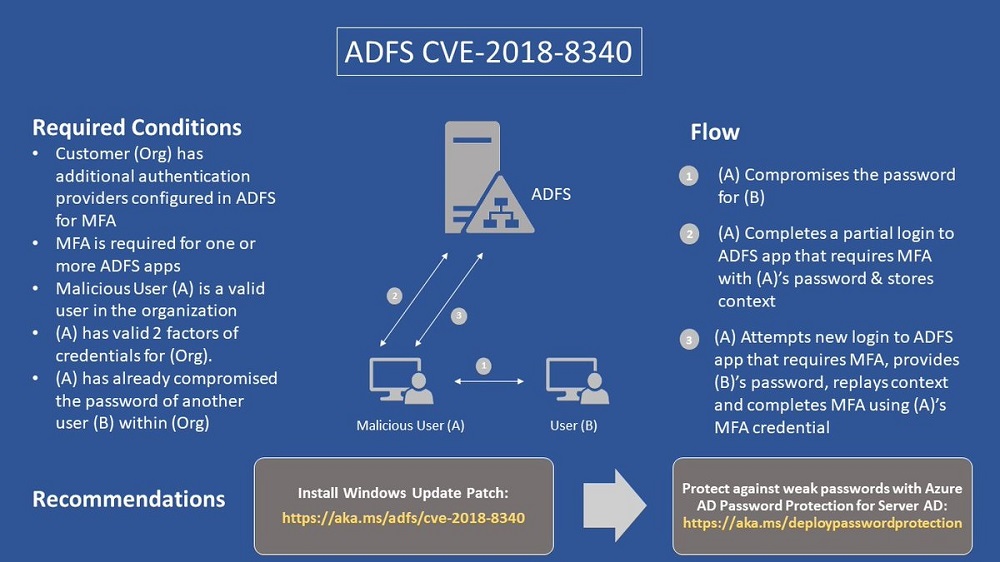
Microsoft has issued patch CVE-2018-8340 to fix a problem with Active Directory Federation Services. You should download and install this patch now.