Microsoft has released limited Graph support for accessing Exchange custom attributes in groups synchronized from on-premises environments. Not every type of Entra group is available on-premises, so we’re really talking about distribution groups and security groups. In any case, real-only access to the fifteen custom attributes is available via Graph API and the Get-MgGroup cmdlet. Now it’s up to you to do something inventive with the information.
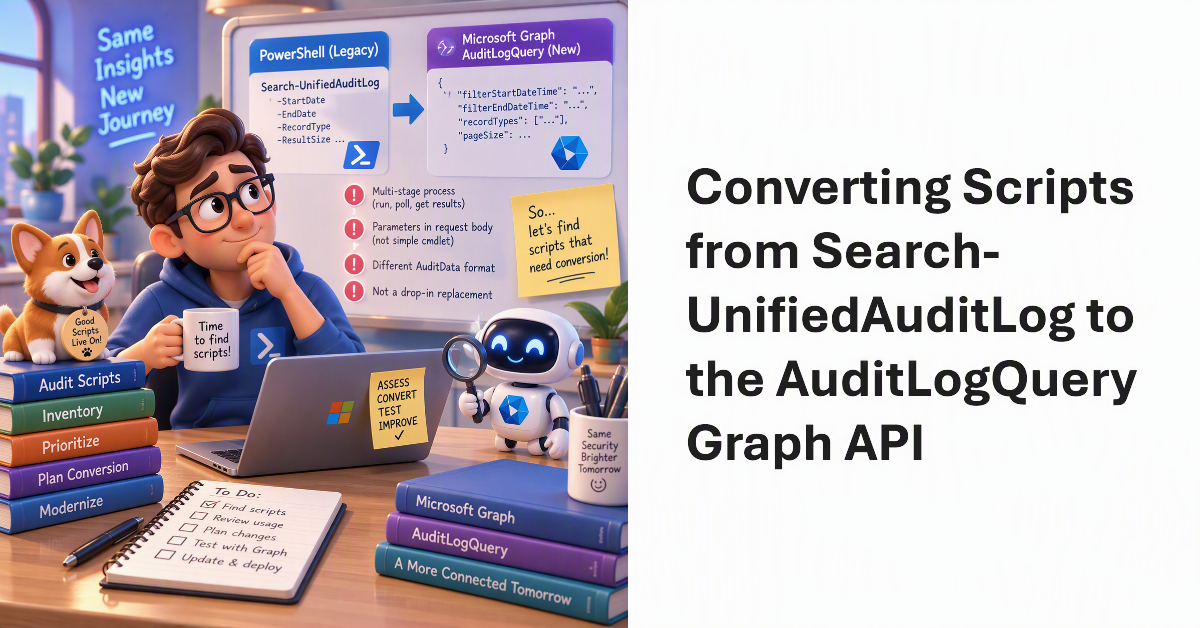
Investigating the work necessary to convert PowerShell scripts based on the Search-UnifiedAuditLog cmdlet to use the AuditLogQuery Graph API shows that it’s not easy. Running audit jobs is a multi-stage process rather than running a simple cmdlet. Parameter values are now passed in a request body, and the properties output in the AuditData payload use a different format. This is definitely not a drop-in exercise, so it’s time to find scripts that need conversion.
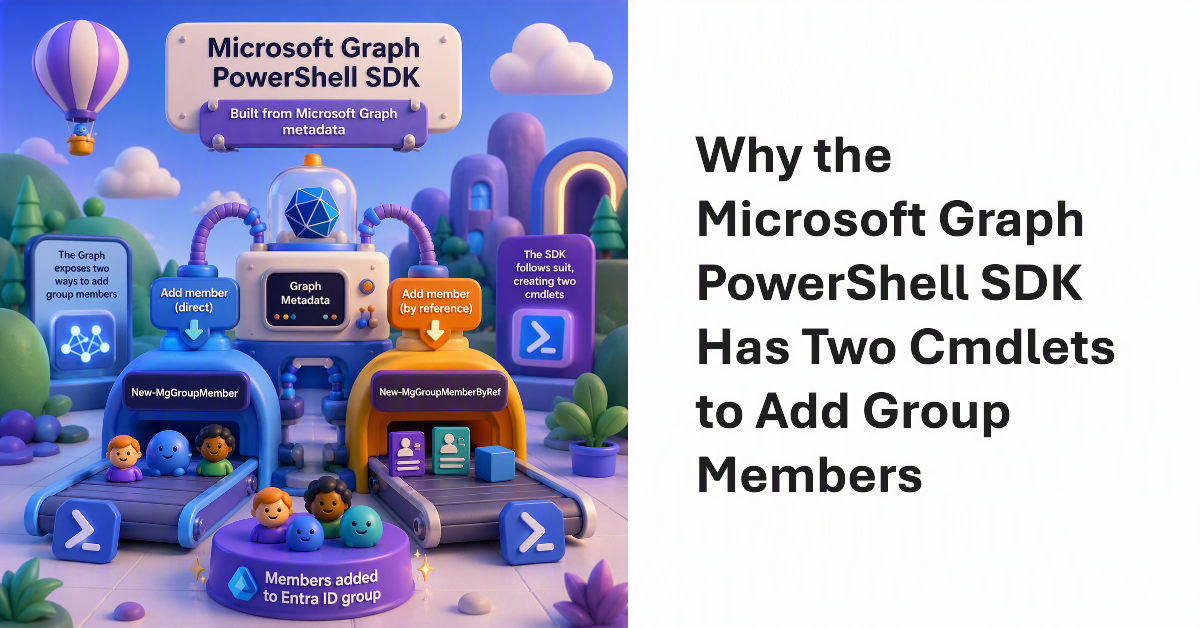
It’s a consequence of how the Microsoft Graph PowerShell SDK is built that two cmdlets are available to add members to Entra ID groups (the same is true for group owners). The reason why the New-MgGroupMember and New-MgGroupMemberByRef cmdlets exist is down to how the Graph SDK build process constructs cmdlets from Graph metadata. The Graph exposes two ways to add new group members, so the SDK follows suit.
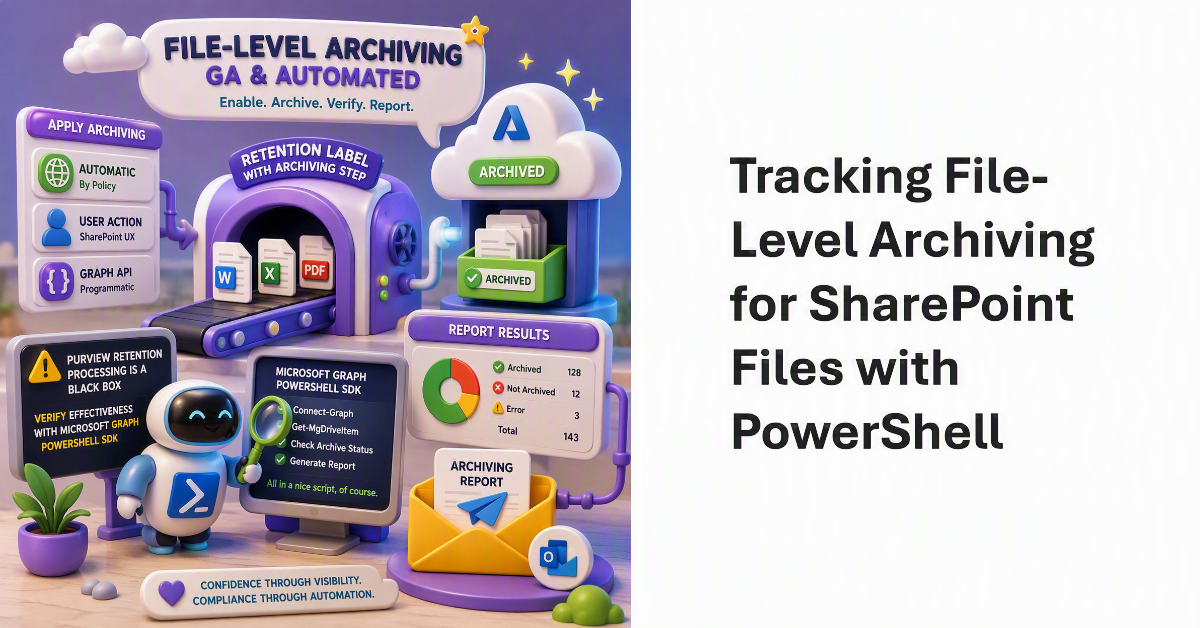
File-level archiving is now generally available and can be applied to files automatically, by users through the SharePoint browser UX, or via a Graph API. The big problem with Purview retention processing is its black box nature, so to discover how effective retention labels with an archiving step are, we use the Microsoft Graph PowerShell SDK to check the archiving status of files and report the results via email. All in a nice script, of course.
If you use the Microsoft Graph PowerShell SDK, you might know that the Graph APIs for SharePoint sites sometimes need a little help. For instance, finding a set of sites to process can be problematic because the APIs do not support extensive filtering capabilities. The solution is to use other Microsoft 365 cmdlets to find objects associated with sites. Inserting an intermediate step might seem crazy, but it can be the most effective way of solving the problem.
The problem with V2.41 of the Microsoft Graph PowerShell SDK that stopped runbooks executing in PowerShell V7 runtime environments was disappointing. However, it was also a good wake-up call for tenant administrators to pay attention to maintaining healthy Azure Automation custom runtime environments. This article proposes a separation between current and production environments and explains how to use PowerShell to get the right modules to the right place.
After saying that the Graph didn’t offer much support for group mailboxes, I was promptly countered with an article explaining how to use the Exchange Import-Export API to access folders and items in group mailboxes that wasn’t limited to just the Inbox. Well, the good news is that the approach works, as seen in a complete script written to prove the case, but whether I would ever use this API for a purpose it was never designed for is quite another matter.
The Microsoft Graph PowerShell SDK has long been plagued by assembly clashes that meant it couldn’t be used in the same session as other Microsoft 365 modules. After Microsoft engineering groups looked at the problem for 18 months, a solution was found by MVP Stephen van Rooij and is now available in V2.41. Apart from an issue with old PowerShell 7 versions, the fix looks solid and the SDK can once again be loaded into PowerShell sessions alongside the Exchange Online and Teams modules.
When launched in 2015, Outlook groups were an email-based collaboration platform. Now called Microsoft 365 Groups, the few Outlook groups that host email-based discussions have a distinctive Graph API to create and manage the conversations, topics, and posts which make up their discussions. This article reviews how to fetch these objects and how to create new conversations and reply to posts (using the Outlook Groups APIs, of course).
Administrators know how to use the default Microsoft Graph Command Line Tools app for delegated interactive Graph sessions. In this article, we cover the topic of using custom Entra ID apps to enable granular access for selected users who need some, but not all, Graph permissions to get their work done. Some changes have taken place in this area due to the advent of WAM, but the concepts and implementation steps are straightforward.
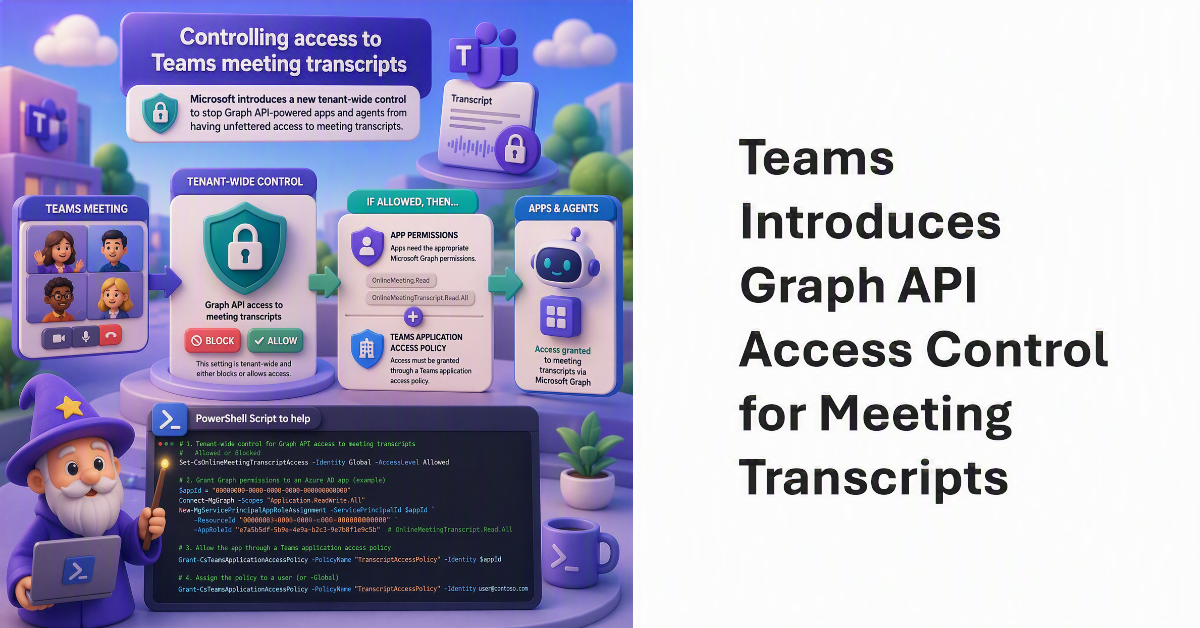
Microsoft has introduced a new control to stop Graph API-powered apps and agents from having unfettered access to Teams meetings transcripts. The new control is tenant-wide and either blocks or allows Graph API access. But after that, apps need the appropriate permissions and access through a Teams application access policy. To help, we illustrate how everything works with a PowerShell script.
On September 16, 2026, Microsoft announced a 12-month retirement period for support of PowerShell V5.1 by the Microsoft Graph PowerShell SDK. Microsoft also announced V3 of the Graph SDK and said that the new version will only support PowerShell V7. The transition for most scripts should be straightforward, but attention needs to be paid when scripts use outdated .NET assemblies. Famous last words…
A reader asked why the Outlook Mail Graph API doesn’t support access to group mailboxes. The basic reason is that a group mailbox doesn’t have an account and the Outlook Mail API only supports mailboxes that are linked to an account. When you look at the current usage of group mailboxes, it doesn’t seem like there’s much data to mine. Maybe the need for Graph API support for group mailboxes isn’t such a big thing?
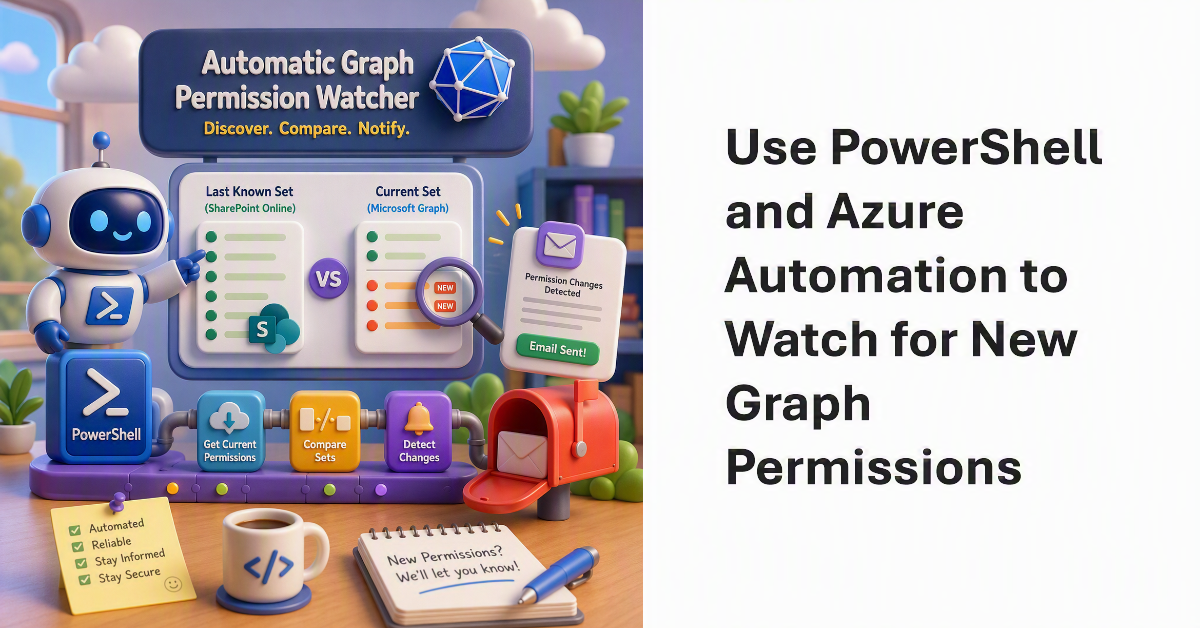
After Microsoft released some new Graph permissions, thoughts turned to how to discover new permissions after they are released. Code is the best way to perform automatic checks, and this article explains how to use PowerShell to check a last known set (stored in SharePoint Online) against the current set. Any variations are reported to administrators via email. It’s nice to automate this kind of operation.
In a GitHub post, Microsoft says that interactive Graph sessions using the default Microsoft Graph Command Line Tools app will use WAM in the future. Some administrators use older versions of the Microsoft Graph PowerShell SDK for continued access to browser-based authentication, but this won’t be possible once Microsoft makes the server-side change to enforce WAM on an undefined future date. Teams and Exchange Online also use WAM, apparently for better security.
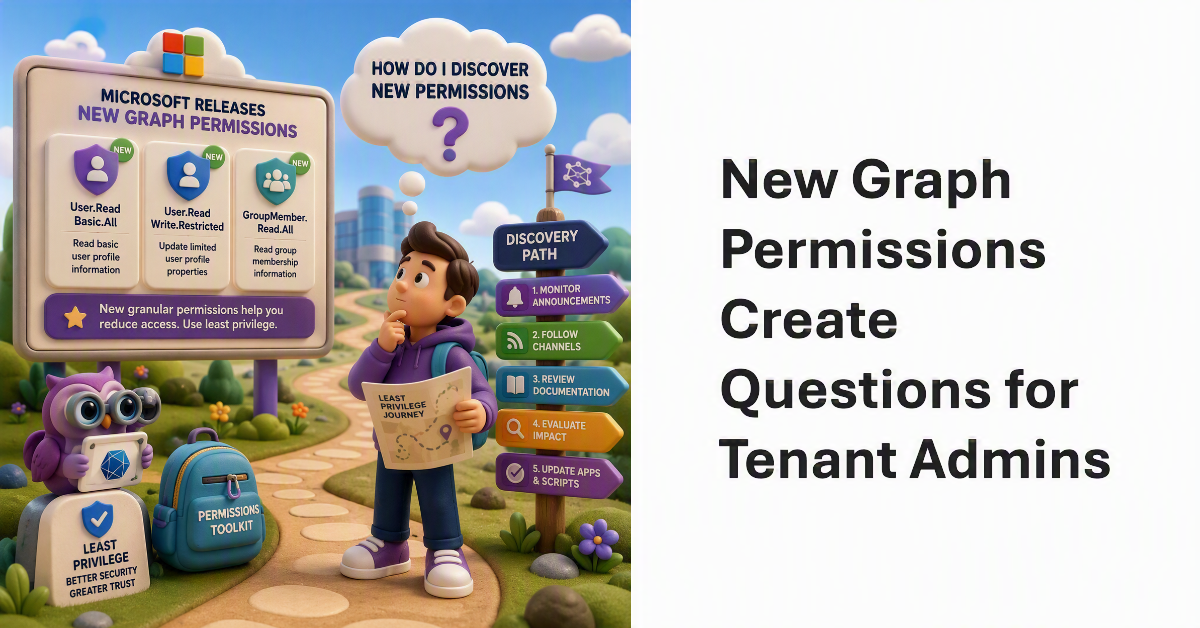
Microsoft issues new granular Graph permissions on an ongoing basis. That’s good, but only if tenants use the permissions to replace wider permissions in apps and scripts. Three new permissions recently became available, including two to reduce what apps can do with user account objects. The question is how to discover when Microsoft releases new permissions so that a decision can be made whether to use the new permissions.
Following up on the primer explaining how to use JSON batching, this article expands on the principles explored in the primer and explains how to permanently remove batches of mailbox items. Removing mailbox items requires more care and attention than updating some Entra ID user accounts, and we explain what the batch commands are to effect both permanent and recoverable deletions. A full working script is available for you to try out.
The Invoke-ChangeMeetingOrganizer cmdlet can transfer meeting ownership from one user to another. In this article, we discuss using a script to transfer meetings in bulk between users. The code requires a mixture of Exchange Online and the Microsoft Graph using a registered Entra ID app. It all sounds complicated, but really isn’t – and the code handles scenarios like transferring meetings from someone leaving the organization.
The Microsoft Graph PowerShell Command Line tools app is how people run Microsoft Graph PowerShell SDK cmdlets. The app can suffer from permissions creep, meaning that over time, the app accrues a set of delegated permissions used by people to access different types of Microsoft 365 and Entra ID information. All is fine until an internal limit is reached, at which point authentication fails and some permissions must be pruned.
JSON batching is one of the most effective ways to speed up the processing of Graph API requests. Although it might seem complicated, once you understand how batches are put together and submitted to the Graph batch endpoint, it’s not that hard. JSON batching is of particular interest to large Microsoft 365 tenants that might need to process tens of thousands of accounts, mailboxes, groups, and so on. All explained here, along with a PowerShell script to show how it’s done.
A user assigned managed identity (UAMI) is a secure method to authenticate with many important endpoints, including the Microsoft Graph. It’s like a system assigned managed identity (SAMI), but the big difference is that a UAMI is an Azure resource that isn’t tied to an automation account. It can be used in multiple areas of Azure and a UAMI might be a better option for large organizations that make extensive use of Azure resources.
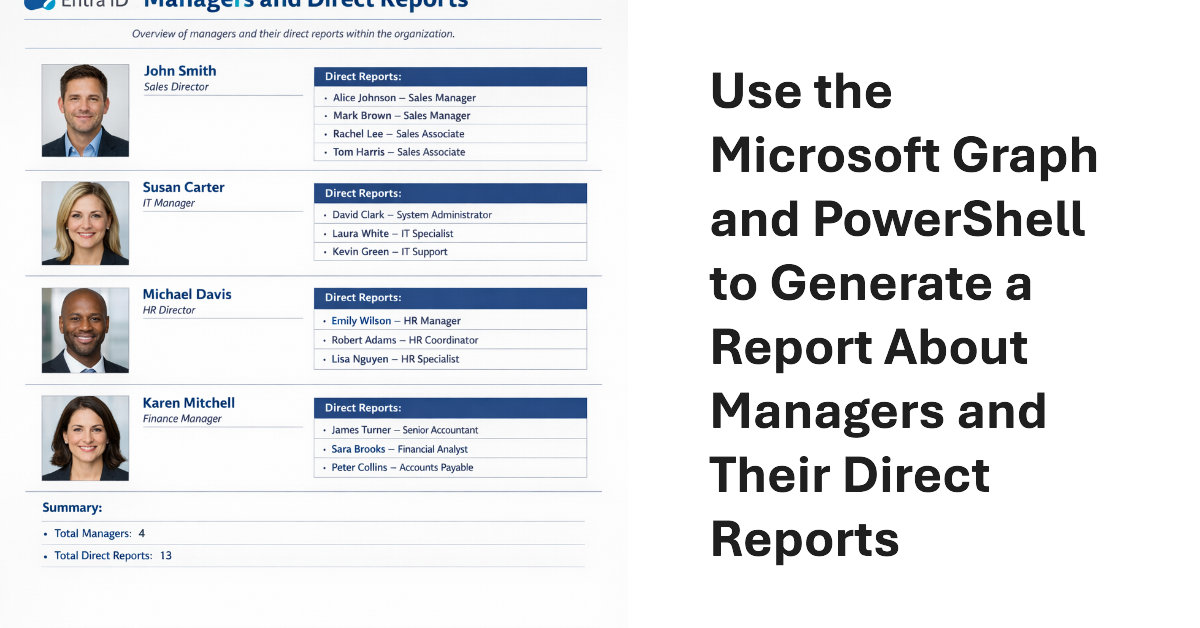
An old article from 2021 written about how to create a report detailing managers and direct reports from Azure AD needs revision. This version uses the Microsoft Graph APIs and explains how to work around a known issue with Graph filtering with a mixture of server-side and client-side filters. It’s the kind of update that PowerShell scripts need when technology change – or when we learn how to do things better.
Delta queries are a Microsoft Graph mechanism to allow applications to query resources to find objects that have changed since a baseline was established. The technique is most useful for applications that need to synchronize a local store with online content. It’s not an appropriate method to use for reporting changes because knowing that an object changed doesn’t mean much by itself.
The third edition of the Automating Microsoft 365 with PowerShell eBook is now available in EPUB and PDF formats. The paperback version will be available on July 1. This 430-page eBook offers the most comprehensive coverage of automating tenant management operations for Microsoft 365 and includes a swathe of practical, worked-out examples to help tenant administrators build scripts to automate tasks.
An app written to fetch details of Copilot interactions from the TeamsMessagesData folder suddenly stopped working when the Graph refused to return items. The 403 forbidden error can’t be argued with. It’s a pain when apps stop working just because of a change made at an API level. Fortunately, the aiInteractionHistory API fills the gap.
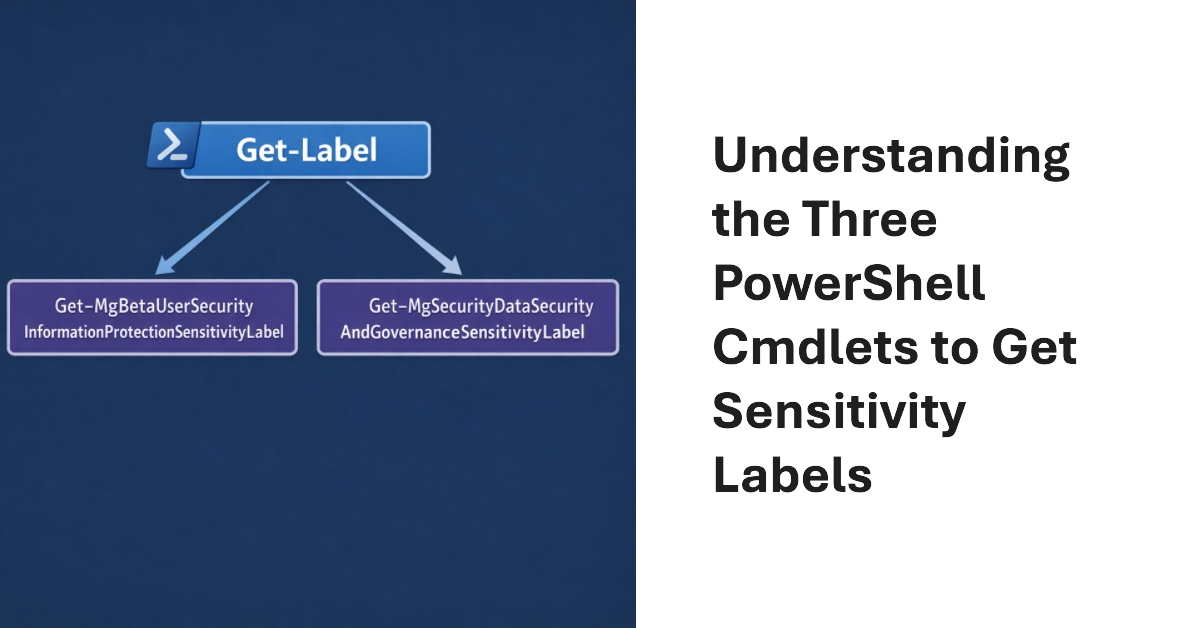
Three cmdlets exist to fetch sensitivity labels. One is in the Exchange Online module; the others are powered by Graph APIs. What are the differences between each method and how can you make sure that the set of sensitivity labels fetched by PowerShell is the full set of available labels? These and other questions are investigated in this article.
Some days ago, I wrote about creating a new employee welcome email with ICS files for corporate events. As it turns out, Inviting employees to attend those events by updating the participant list with PowerShell is an easier and better approach. This article explains how to find calendar events, update participant lists, and update events with the Microsoft Graph PowerShell SDK.
Understanding what Graph permissions are required by apps can be challenging. In this article we discuss how the Group.Read.All and GroupMember.Real.All permissions work and why you should choose one permission over the other and respect the principle of least permission when it comes to assigning Graph permissions to your apps and PowerShell scripts.
This article discusses how to list files archived using the SharePoint Online file-level archiving feature. We also discuss how to archive and unarchive files using the Microsoft Graph PowerShell SDK and Graph API requests. As it turns out, the drives API is the best way to find (list) archived or unarchived files, while archiving files that haven’t been modified in a while is easy with a few lines of PowerShell.
Now rolling out to Microsoft 365 tenants is the ability to update user profile cards with details of awards and certifications held by users. Usually this would be done through a Copilot connector, but it’s possible to add awards and certifications using Microsoft Graph PowerShell SDK cmdlets. All explained in great detail with working examples here.
The additionalProperties property is available for many Microsoft Graph PowerShell SDK cmdlets. In this article, we explain the function of the additionalProperties property and how it functions in holding output for Microsoft Graph PowerShell SDK cmdlets. It’s all because of the lack of strongly typed properties, or so the AutoRest process would have us believe.
A reader wanted a weekly incomplete task digest to send details of Planner tasks to people with outstanding work to do. We used PowerShell to scan for incomplete tasks for people who are members of a group, perform some analysis on the data, and create and send email. Despite some deficiencies in the Planner Graph API, the code is pretty straightforward.
Microsoft has announced details of a change to app permissions to restrict updates to sensitive message properties (like recipients) without consent for a new advanced mail access permission. If tenants have apps that interact with message properties, including apps developed by third parties, they should check whether the apps are updating sensitive properties. If so, the new permission must be assigned or the apps will stop working.
The April 2026 update for the Automating Microsoft 365 with PowerShell eBook is now available for subscribers to download. Refreshed EPUB and PDF files can be downloaded from Gumroad.com. The Kindle and paperback editions are also updated. This month we reflect on V2.36.1 of the Microsoft Graph PowerShell SDK and why so little has changed in this important component.
It’s easy to remove sensitivity labels from SharePoint Online files when only a few files are involved. Doing the same task at scale requires automation. In this article, we explain how to use the Microsoft Graph PowerShell SDK to find and remove sensitivity labels from files stored in SharePoint Online and OneDrive for Business.
Shared mailboxes are not CRM systems. However, many Microsoft 365 tenants use shared mailboxes to handle customer queries and then want to measure KPIs such as agent responsiveness to customer queries or the number of queries handled per agent in a month. As explored in this article, it’s possible to use the Microsoft Graph to extract some KPI-like data from shared mailboxes.
This article explains how to use scoped Graph permissions to restrict app access to lists and list items in SharePoint Online and OneDrive for Business sites. It’s a follow-up to other articles covering how to restrict app access to SharePoint Online sites and files. Scoping app access to specific objects is important because otherwise apps can access everything in SharePoint Online, and that isn’t good.
Update #21 for the Automating Microsoft 365 with PowerShell eBook is now available for current subscribers to download from Gumroad.com. Refreshed PDF and EPUB files are available and the paperback version available from Amazon.com is also updated. Automating Microsoft 365 with PowerShell is packed with practical ready-to-use examples of working with apps, sites, mailboxes, teams, plans, and other data. Every Microsoft 365 administrator should have this book!
Dev Proxy is a Microsoft tool built to help developers figure out the most effective way of using Microsoft Graph API requests. On the surface, Dev Proxy doesn’t seem like a tool that would interest people who use the Microsoft Graph PowerShell SDK to write scripts for Microsoft 365. But all tools have some use, and Dev Proxy can help.
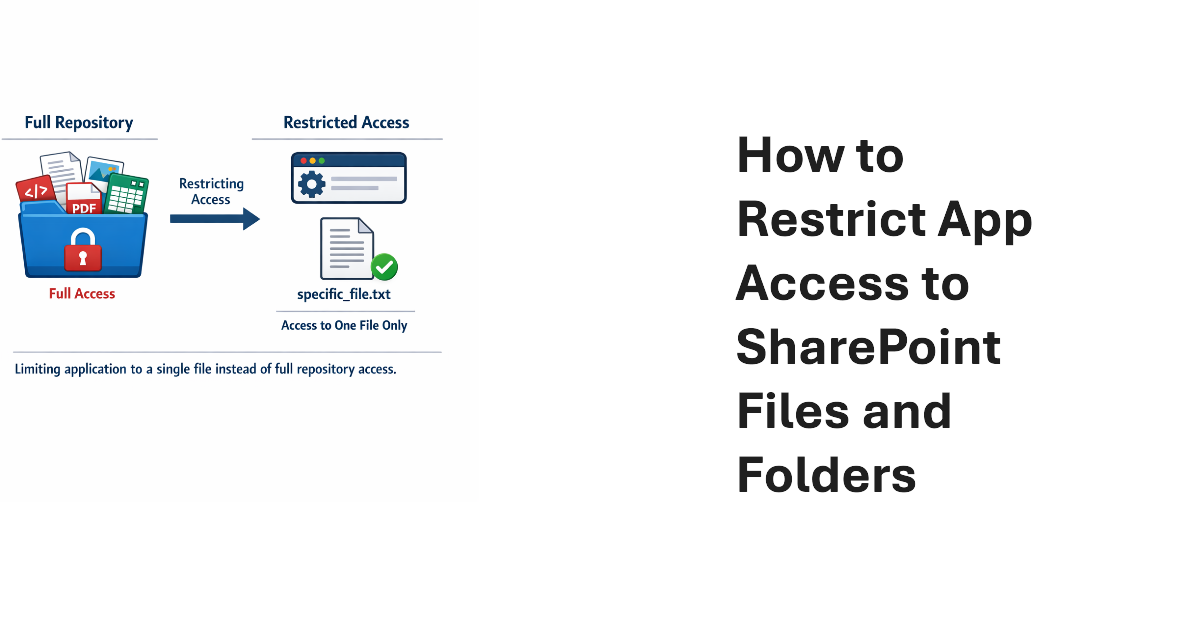
Scoped permissions grant apps granular access to files and folders in SharePoint Online and OneDrive for Business sites using the Files.SelectedOperations.Selected Graph permission. The permission allows apps to access specific files or all the files in a folder. It’s a great way to make sure that apps don’t have unfettered access to confidential documents. Not that any app would try to have that kind of access…