Conditional access policy plans are now available in preview. The idea is to define common rules, conditions like breakglass accounts and have the details inherited by CA policies. Microsoft provides a migration facility to move existing policies to plans, but it’s probably going to take some time for tenants to inventory their current CA policies, understand points of commonality, and slowing move towards rationalization.
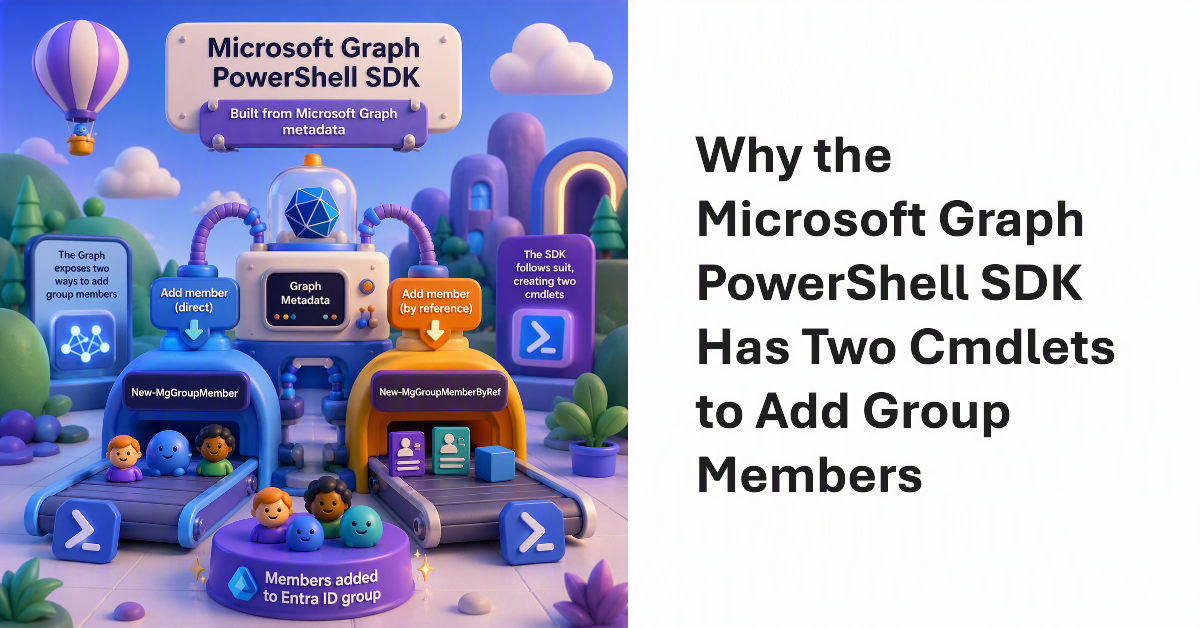
It’s a consequence of how the Microsoft Graph PowerShell SDK is built that two cmdlets are available to add members to Entra ID groups (the same is true for group owners). The reason why the New-MgGroupMember and New-MgGroupMemberByRef cmdlets exist is down to how the Graph SDK build process constructs cmdlets from Graph metadata. The Graph exposes two ways to add new group members, so the SDK follows suit.
The Entra admin center will soon get a new user role permission to control whether users can create agent blueprints. The control will be enabled by default. I think this is a terrible idea. Outside the hallowed walls of Microsoft, does the need really exist to allow average users to create agent blueprints? I don’t think so. Agents are like apps. They need to be controlled and managed by people who know what they are doing.
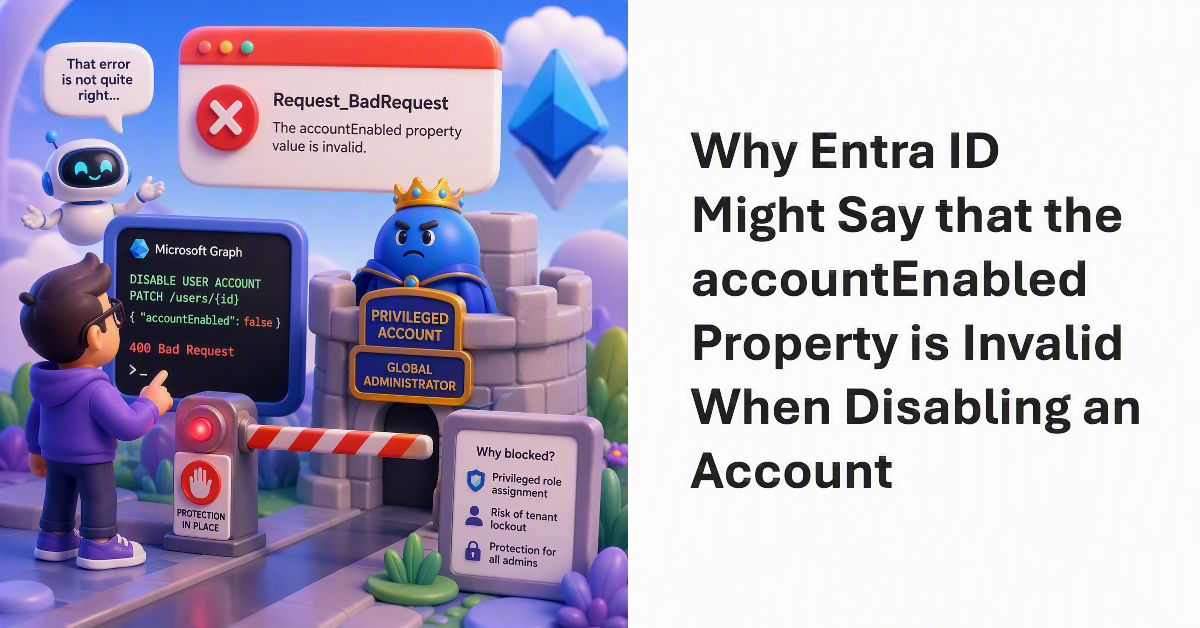
When attempting to disable a user account in an interactive Graph session, I was told that the command failed because the accountEnabled property was invalid. The error is obviously incorrect because it’s very possible to update the property to disable or enable an account. However, different rules apply when the account is holds a privileged role, like Global Administrator. Entra imposes some reasonable blocks, even if the error messages are not good.
Continuous Access Evaluation (CAE) is supported by core Microsoft 365 workloads like Exchange Online, SharePoint Online, and Teams, and the reach of CAE is gradually spreading throughout the Microsoft cloud ecosystem. However, security researchers report inconsistent coverage across first-party apps and clients that take a little gloss off the promise of instant access revocation when critical events like user password changes happen.
After the discussion about the licensing gap prompts shown in the Entra admin center, here’s a PowerShell script to compute the set of user accounts that should have Entra P1 licenses. The information comes from the conditions property of conditional access policies with group and directory role membership expanded to find individual accounts. The set is checked against the set of users licensed for Entra P1 to find the accounts that need to be licensed.
The Entra admin center is flagging licensing gaps for conditional access. The messages are informational, not the beginning of a new automated billing procedure to charge tenants when Entra ID notices that some accounts use conditional access policies when they don’t have a license. In this article, we discuss the product license insight and how Microsoft measures conditional access usage, and show how to use PowerShell to find who’s using conditional access
MC1448379 (5 August 2026) announces the retirement of the MemberOf rule operator from Entra ID in early November 2026. The removal of the rule operator might affect the membership rules used for dynamic groups, dynamic administrative units, and auto-assigned entitlement management policies. If a tenant doesn’t act, Entra ID will stop processing the rules and memberships will become increasingly inaccurate. And that’s a bad thing!
A new Entra ID feature enables the ability to block nesting for security groups. In other words, you can’t include other groups as members of a group. That might not sound important, but it is to those who manage permissions, especially when the time comes to figure out who exactly has access to something confidential. The new feature isn’t fully implemented yet, but it should be very valuable when it’s fully deployed to tenants.
In an important announcement for all tenants, Microsoft revealed that Entra ID will no longer provide SMS one-time codes or voice calls for MFA challenges after February 1, 2027. Tenants can continue to use telephony-based authentication methods after that date, but only by purchasing a service from a telecom provider. This is arguably the biggest change in Entra ID authentication since mandatory MFA for administrative interfaces – and we have a PowerShell script to help identify the affected accounts.
An old article from 2021 written about how to create a report detailing managers and direct reports from Azure AD needs revision. This version uses the Microsoft Graph APIs and explains how to work around a known issue with Graph filtering with a mixture of server-side and client-side filters. It’s the kind of update that PowerShell scripts need when technology change – or when we learn how to do things better.
Delta queries are a Microsoft Graph mechanism to allow applications to query resources to find objects that have changed since a baseline was established. The technique is most useful for applications that need to synchronize a local store with online content. It’s not an appropriate method to use for reporting changes because knowing that an object changed doesn’t mean much by itself.
The third edition of the Automating Microsoft 365 with PowerShell eBook is now available in EPUB and PDF formats. The paperback version will be available on July 1. This 430-page eBook offers the most comprehensive coverage of automating tenant management operations for Microsoft 365 and includes a swathe of practical, worked-out examples to help tenant administrators build scripts to automate tasks.
Microsoft is closing a gap in conditional access policies where apps that only request baseline scopes with at least one exclusion are not processed. The rollout has already started and should be finished by mid-August. For most tenants, the change shouldn’t be an issue, but it is possible that some apps are in use that fit the profile and cannot handle conditional access. If MC1223829 appeared in your tenant, it’s time to check.
Microsoft plans to improve the security of the Self-Service Password Reset (SSPR) facility in September 2026 by requiring users to register at least one authentication method. SSPR will then use the registered authentication method to verify user accounts when changing passwords. The change aligns SSPR with user sign-ins and improves security by removing fallback on directory attributes, which might be altered by attackers.
A recent blog from the Microsoft Digital (IT department) discusses the preview implementation of container management labels for security groups. The implementation is limited because it encompasses just one control: the ability to have guest accounts in the membership of security groups. However, just that limited control is sufficient to stop unintended access to sensitive information by guest accounts, and that’s a very good thing.
License insights is a new feature in the Entra admin center. The Microsoft 365 admin center also shows some license insights in a dashboard card. The two views don’t line up. This isn’t very surprising because different teams generated the information, but it would sure be nice if Microsoft delivered comprehensive license reporting for Microsoft 365 tenants, including the Entra premium licenses.
Entra ID uses an eventually consistent multi-region database architecture. PowerShell code that fetches and updates Entra ID objects needs to interact with the database in the most efficient manner. This article illustrates some guidance from Microsoft engineering with examples from the Microsoft Graph PowerShell SDK. I’m sure your scripts already use these techniques, but if not, we have some helpful pointers.
User and Group assignments can be added to Entra ID applications. Once assignments exist for an application, only assigned users can access that application. This method is a good way to secure access to applications that have consent to use high-profile permissions like Sites.FullControl.All or Mail.Read. Microsoft 365 tenants should consider how to use assignments to control user access to applications.
Microsoft disclosed that Entra ID login events were missing from Microsoft Defender for Cloud Applications for nine months — and waited more than three months after the fix to tell customers. Here’s why that matters and what you should do about it.
Microsoft released the preview of the Entra ID Backup and Recovery solution to tenants on 19 March 2026. Although the software is functional in tenants, Microsoft didn’t make a big announcement. We’ve spent the last few days testing backup and recovery and put together the major points about the new solution, which is doubtless going to be welcomed by tenants if not by backup ISVs.
This article explores how to use Entra ID audit records to create a weekly report about role assignment additions and deletions. After deciphering the information contained in the audit records, it’s easy to generate a report showing who made the assignments and if any critical role assignments are in the mix. We can then email the report to interested parties, all with some relatively simple PowerShell.
Microsoft is rationalizing the options to revoke sessions for a user account in the Entra admin center by removing an old revoke MFA sessions button. That seems like a perfectly reasonable thing to do. When administrators want to revoke sessions for an account, the best way is to create a PowerShell script to perform the necessary steps. That way you don’t need to worry about buttons.
Microsoft has released a set of security benchmark recommendations for Microsoft 365 tenants that it calls baseline security mode. The recommendations cover authentication, file access, and Teams and the idea is that these are settings that Microsoft believes have proven their value over the years. The only criticism that you might have is about the potential clash for conditional access policies, but that’s not serious.
The Entra ID Governance solution includes a workflow to detect and remove inactive user accounts. Sounds good, but the same can be done with PowerShell if you want to avoid the cost of Entra ID Governance licenses or want to create a bespoke workflow that’s better suited to the business needs of the organization. Azure Automation would be a good way to process this workflow.
Entra ID has long supported soft-deleted Microsoft 365 Groups. Now support is available to list and restore soft-deleted security groups in both the Entra admin center and cmdlets from the Microsoft Graph PowerShell SDK. The update is very welcome as it fixes a big recovery gap in the Entra ID story. Too many important security groups have been deleted in error, much to the chagrin of administrators.
The Entra ID password protection policy contains settings that affect how tenants deal with passwords. Entra ID includes a default policy that doesn’t require additional licenses. Creating a custom password protection policy requires tenant users to have Entra P1 licenses. As explained in this article, once the licensing issue is solved, it’s easy to update the policy settings with PowerShell.
A recent change has exposed the applications used by the My Sign-ins portal for use in conditional access policies. This article discusses the app-centric nature of Microsoft 365 and Entra ID and why it’s important that the newly-revealed set of applications are available for conditional access processing, just in case the Entra ID agents planned by Microsoft can’t optimize your policies.
Guest account management should be a part of every Microsoft 365 tenant administrator’s checklist, unless the tenant has no guests. That’s possible but given the way that workloads like Teams and SharePoint Online create new guest accounts, the average tenant is likely to have quite a few guests. The question is how to manage guests – with Microsoft’s tools or using tenant-designed PowerShell scripts?
The Entra ID Keep Me Signed In (KMSI) feature creates persistent authentication cookies to allow users to avoid sign-ins during browser sessions. Is this a good or bad thing and should Microsoft 365 tenants enable or disable KMSI. I think KMSI is fine in certain conditions and explain my logic in this article. Feel free to disagree!
The Org Settings section of the Microsoft 365 admin center has a new People Settings section where you can choose properties for the Microsoft 365 profile card instead of using PowerShell. The kicker is that the old method of using Exchange custom properties to customize what appears on the profile card is being replaced with standard Entra ID properties. A migration is needed, and it’s easily done with PowerShell.
Three new Graph API resources provide easy access to Entra ID authentication method summary data. The information is helpful to understand the type of sign-ins that happen, and the authentication methods used by user connections. The article includes a script based on the MFA sign-in summary to highlight non-MFA connections and the apps users connect to.
If you use the Microsoft Graph PowerShell SDK, you don’t need to worry about obtaining an access token because SDK cmdlets include automatic token management. Although you don’t need to know the details of the access token used in an SDK session, it’s possible to find and examine its contents, and even use the token with a Graph request. It’s a nice to know thing that you’ll never need in practice.
The Conditional Access Optimization Agent is one of 6 Security Copilot agents unveiled by Microsoft on March 24, 2025. The idea is that the agent can optimize CA policies by observing the connectivity behavior within a tenant. The agent can suggest how to fill gaps in CA coverage, detect new users and apps, and generally be helpful. Is it worth it? Experience will tell…
Microsoft 365 users can connect their OneDrive for Business account to ChatGPT. This is not a great thing because it exposes the potential for sensitive corporate information to be exposed outside the organization. How can you block ChatGPT Access to OneDrive? The best way is to stop people from using the ChatGPT app. If that’s not possible, make sure to encrypt confidential files with sensitivity labels.
A new people administrator role is available in Entra ID. The new role allows holders to manage settings associated with people, like pronouns and custom properties for the Microsoft 365 user profile card. The people administrator role is a less privileged way to assign responsibilities for people actions and removes the need to assign more privileged roles like User administrator. Time for a role review!
Entra ID allows unprivileged users to update the user principal name for their accounts via the admin center or PowerShell. It seems silly because no justification for allowing people to update such a fundamental property is evident. Perhaps Microsoft has some excellent logic for allowing such updates to occur, but blocking access seems like the right thing to do.
This article describes how to create eligible and active PIM role assignment requests using cmdlets from the Microsoft Graph PowerShell SDK. Although the PowerShell code is straightforward, Microsoft recommends using the Entra admin center for Privileged Identity Management. But you can automate the management of role assignment requests if you want to.
MC705357 (9 Jan 2024) says that the dynamic group rule builder in the Entra ID and Intune admin centers no longer supports the contains and notContains operators. There’s no real cause to worry because existing rules continue to work and if you need to use contains or notContains in a membership rule, you can edit the rule manually.
A question came in about how to report admin consent requests as viewed through the Entra ID admin center. PowerShell does the trick, once you know how. The key thing is to find the right cmdlet to use. Once you know that, the rest is pretty easy as we explain in this article.